← All services
Is your Lovable app leaking data? Security audit and fix for Lovable, Bolt, Base44 and Replit apps

Security Audit & Fix for AI-Built Apps (Lovable, Bolt, Base44, Replit)

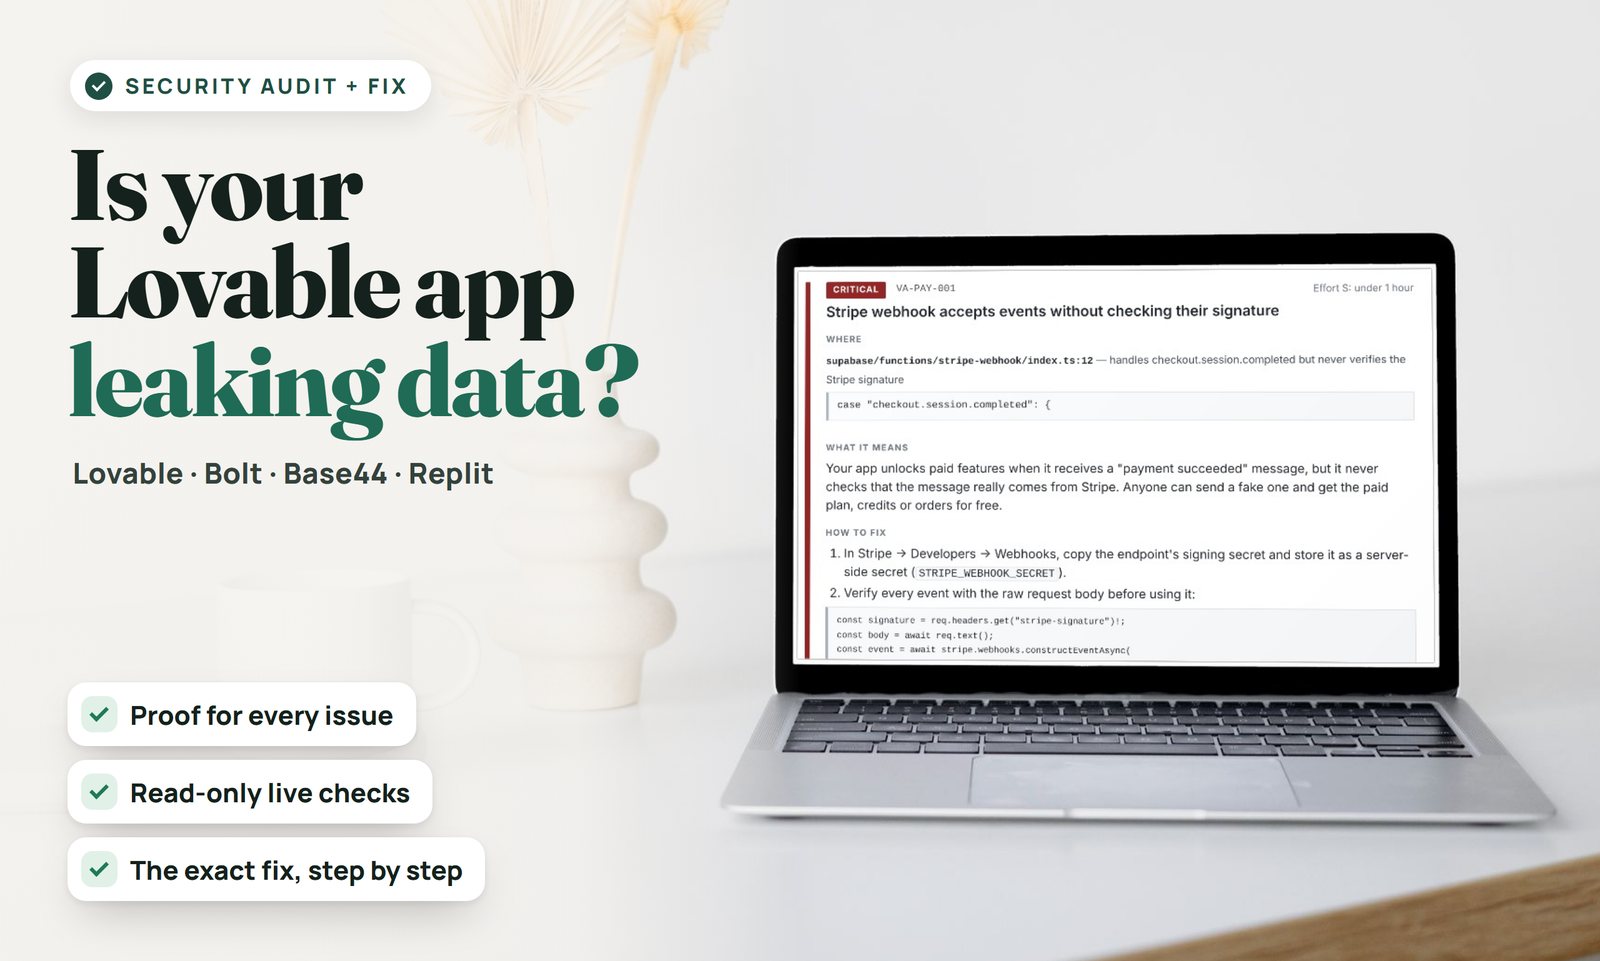
Apps built with Lovable, Bolt, Base44 or Replit can work in a demo and still leave data open in production: database tables anyone can read, secret keys in the browser, payment webhooks anyone can fake, AI features anyone can run on your bill.

Report in 2 days · read-only live checks
Why it matters

In our scan of 40 public apps built with Lovable and Bolt on Supabase (November 2026), 17 had at least one critical issue and 33 at least one high-severity issue.

We review your code and, with your signed consent, your live app. You get a report a non-developer can read in a few minutes, with proof for every problem and the exact fix.

  • Live checks only read, never change anything, and run only after you sign a short authorization
  • We never ask for your passwords or your Supabase secret key
  • Fixes go on a separate branch of your code, and you approve them before they go live

Choose your package

Total today$145

Secure payment by Stripe. We never ask for your passwords or secret keys.

Vibe-coded app security

Where AI-built apps leak

Most Lovable and Bolt apps talk to Supabase straight from the browser, with a public key anyone can copy. The database’s row-level security (RLS) rules are then all that stands between a stranger and your users’ data. Our Supabase RLS audit reads every table, policy and function, then we check the rest:

  • Supabase: row-level security, policies, storage buckets, database functions, views, Edge Functions and auth settings
  • Secrets: keys in your code, .env files, git history and the live JavaScript
  • Payments: Stripe webhook signatures, prices taken from the browser, paid status set from the browser
  • Cost: AI providers called from the browser or from unprotected functions
  • And: Firebase rules, exposed files, security headers, source maps, vulnerable dependencies

You get the report as a self-contained HTML file and a PDF.
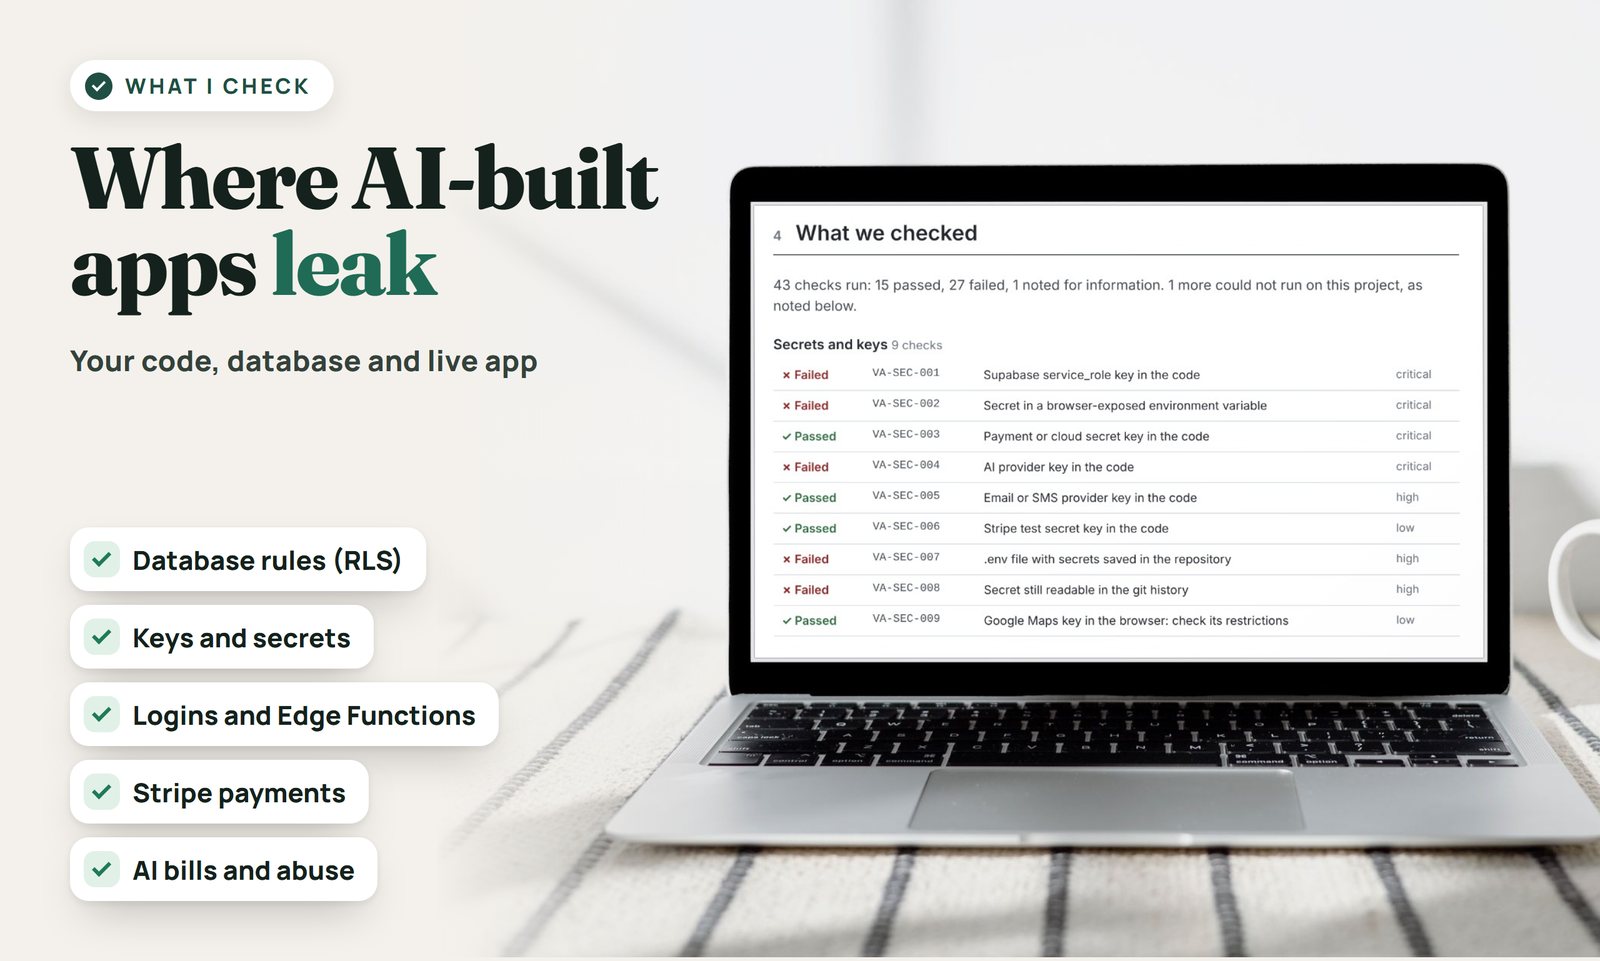
What we check in AI-built apps: database rules (RLS), keys and secrets, logins and Edge Functions, Stripe payments, AI bills and abuse
Packages

Fixed prices, no surprises.

If the report shows more work than your package covers, we send you a quote for the rest before doing anything extra.

Security scan + report
Find out what is open
$145one-off
Delivered in 2 days
  • Code and database review
  • Live read-only check, with your signed consent
  • Report with proof, plain-English explanation and fix steps
  • A priced quote for every fix
Choose this package
Audit + urgent fixes
Close the serious holes
$395one-off
Delivered in 5 days
  • Everything in the scan + report
  • Critical and high issues fixed, up to about 4 hours of work
  • Re-scan after the fixes, with a before/after summary
  • Handover note for you or your developer
Choose this package
Full hardening + 1 month monitoring
Fix everything that matters
$795one-off
Delivered in 10 days
  • Everything in Audit + urgent fixes
  • Everything above “info” fixed, up to 10 hours of work
  • Monthly re-scan and alert on new critical issues: first month included
Choose this package
Monitoring only
Keep it closed, after the audit or on its own
$49/ month
Cancel at any time
  • A re-scan of your code and live app every month
  • A short report of what changed
  • An alert within 24 hours if the scan finds a new critical issue
  • Ends at the end of the paid month when you cancel

Secure payment by Stripe · each new prompt to your builder can reopen a hole, so monitoring re-checks your app every month
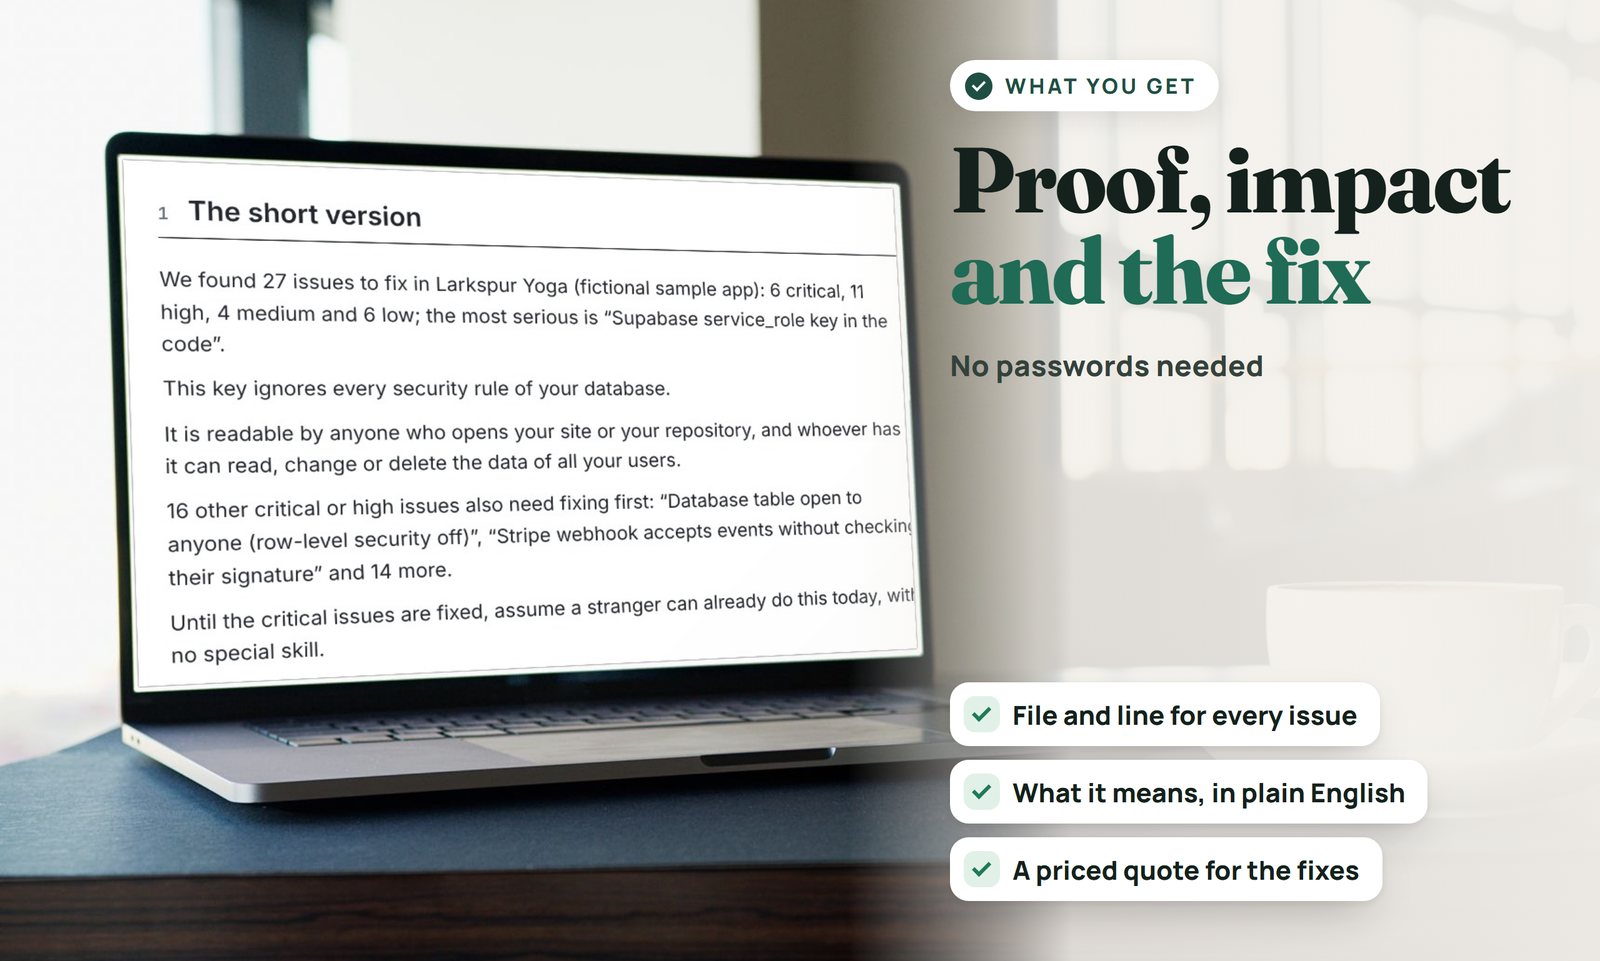
Sample security report: the short version, with proof, impact and the fix
What you get

Proof, impact and the fix

  • Every problem with proof: the file and line, or the live response
  • What it means for your business, in plain English
  • The exact fix, for us or your developer to apply
  • A priced quote for the fixes

See it for yourself: a short sample report, made on a fictional app.

Download the sample report (PDF)

7 pages: the summary, the 3 most serious findings in full, what we checked and the method.

How it works

Nothing changes without you.

  1. Order, or ask first. Pick your package and pay securely by Stripe, or message us on WhatsApp first.
  2. Share what we need, safely. We email you a short guide: read-only access to your code, your app’s address, your Supabase project URL and public key.
  3. Sign the authorization. One page that says exactly what the live checks may do. No live check runs before it is signed.
  4. Get your report. Every problem with proof, what it means, the fix and a priced quote.
  5. Fixes, if ordered. Made on a separate branch of your code. You approve them, then we re-scan and hand over a short note of what changed.

What we need from you

  • Read-only access to your code: GitHub read access, or a zip of the project
  • The address (URL) of your live app
  • Your Supabase project URL and anon (publishable) key: the public key your app already sends to every visitor
  • The signed authorization for the live checks

Using Firebase instead of Supabase? Send the Firebase project ID.

Never send us

  • Your passwords, for any service
  • Your Supabase service_role key, or any key starting with sb_secret_
  • Your database password or connection string
  • Your Stripe secret key, or keys for AI or email services
  • One-time login or two-factor codes

If one is sent by mistake, we tell you and delete it, and you should change it straight away.

FAQ

Lovable, Bolt and Supabase security: questions, answered.

Do you need my passwords?
No. We need read-only access to your code, the app’s address, and your Supabase project URL and public (anon) key, which is already visible in your app. Never send your passwords, your Supabase service_role or secret key, or your database password. We send you a short guide after you order.
Will you change anything in my live app or database?
Not during the audit. The live checks only read what anyone on the internet can already see, and they run only after you sign the authorization. Fixes are made on a separate branch of your code, and you approve them before they go live.
What exactly does the live check do?
Only what any visitor could do with your app’s public key: load your pages and JavaScript, ask each table for at most one row (we record the row count and column names, never the values), list your storage buckets, read the sign-up settings and security headers, and request a few well-known paths such as /.env. At most 2 requests per second. It never creates, changes or deletes anything, never logs in, and never uses a secret key, even one found exposed. If data is already open to the public, we tell you within 24 hours.
My app was built with Lovable, Bolt, Base44 or Replit. Can you still work on it?
Yes. The best case is code we can read, for example a GitHub repository connected to your builder. If your builder does not let you export the code, we can still check the live app, but the report covers less. We tell you which before you pay for fixes.
Lovable and Supabase already have a security scanner. Why pay for this?
Those tools are free and worth running. What we add is proof that each problem is real (the file and line, or the live response), what it means for your business, and the fix, which we can apply and re-check.
Does a clean report mean my app is safe?
No audit can promise that. It means the problems we check for were not found on that date. Apps can change every time you prompt your builder, which is why monitoring exists.
What if my app needs more work than the package covers?
We send you a quote for the rest, based on the report, before doing anything extra. Nothing extra starts until you accept it.
Can I cancel monitoring?
Yes, at any time. Monitoring ends at the end of the paid month.
Service terms

The short terms of every order

They apply together with our Terms of Sale; where they differ, the Terms of Sale win. Nothing here limits your statutory rights.

Scope
Audit: a review of the code you share and, only with the signed authorization, read-only checks of the live app and its Supabase or Firebase project, as listed in the report’s “What we checked”. Fixes: the changes in your package or an accepted quote, made on a separate branch of your code (or as instructions if we have no write access), then a re-scan and a handover note. Monitoring: a monthly re-scan of the same code and live app, a short report of what changed, and an alert within 24 hours when the scan finds a new critical issue. Not included unless agreed in writing: penetration testing beyond the read-only checks, load testing, legal or compliance advice (GDPR, HIPAA, PCI DSS), incident response, contacting your users or authorities, and systems not listed in the authorization.
Your part
You confirm you are allowed to share the code and to authorize the live checks. You share only what we ask for, never passwords or secret keys. You review and approve fixes before they go live. Deploying, and rotating keys in third-party dashboards (Supabase, Stripe, AI providers), are done by you or with you present, following the handover note.
Confidentiality
Everything you share, and everything we find, is confidential and used only for your order. Findings are never published, and your name is never used as a reference or example without your written permission. Sample reports are made from fictional apps only.
Data handling
The copy of your code is used only for the work and deleted after delivery. The dependency check sends your list of packages and versions (not your code) to the public npm registry; tell us if you prefer to skip it. We never record row values from your database, and secrets are masked in the report. The report and its data file are kept for 90 days, then deleted; ask us any time for earlier deletion. Remove our repository access when the work ends.
No guarantee
An audit lowers risk; it is not a guarantee that no other flaw exists. The report covers the checks listed in it, on the code and app as they were on the audit date. Later changes, including new prompts to an AI builder, can introduce new problems. Fixes address the findings listed in the handover note. Our total liability for an order is limited to the amount paid for it, to the extent the law allows.
Payment
Payment by Stripe before work starts, at the price of the package or the accepted quote. Extra work starts only once its quote is accepted and paid. Monitoring is billed monthly and can be cancelled at any time; it ends at the end of the paid month.
Security audit + fix

Find out what your app leaves open.

Order the audit today, or ask us first on WhatsApp.

Team Growtoria

All services